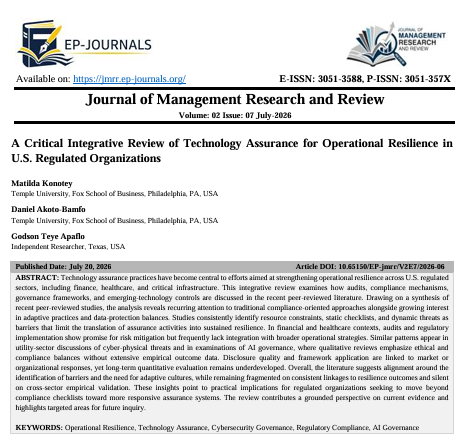
A Critical Integrative Review of Technology Assurance for Operational Resilience in U.S. Regulated Organizations
DOI:
https://doi.org/10.65150/EP-jmrr/V2E7/2026-06Keywords:
Operational Resilience, Technology Assurance, Cybersecurity Governance, Regulatory Compliance, AI GovernanceAbstract
Technology assurance practices have become central to efforts aimed at strengthening operational resilience across U.S. regulated sectors, including finance, healthcare, and critical infrastructure. This integrative review examines how audits, compliance mechanisms, governance frameworks, and emerging-technology controls are discussed in the recent peer-reviewed literature. Drawing on a synthesis of recent peer-reviewed studies, the analysis reveals recurring attention to traditional compliance-oriented approaches alongside growing interest in adaptive practices and data-protection balances. Studies consistently identify resource constraints, static checklists, and dynamic threats as barriers that limit the translation of assurance activities into sustained resilience. In financial and healthcare contexts, audits and regulatory implementation show promise for risk mitigation but frequently lack integration with broader operational strategies. Similar patterns appear in utility-sector discussions of cyber-physical threats and in examinations of AI governance, where qualitative reviews emphasize ethical and compliance balances without extensive empirical outcome data. Disclosure quality and framework application are linked to market or organizational responses, yet long-term quantitative evaluation remains underdeveloped. Overall, the literature suggests alignment around the identification of barriers and the need for adaptive cultures, while remaining fragmented on consistent linkages to resilience outcomes and silent on cross-sector empirical validation. These insights point to practical implications for regulated organizations seeking to move beyond compliance checklists toward more responsive assurance systems. The review contributes a grounded perspective on current evidence and highlights targeted areas for future inquiry.
References
1) Anderson, C., Baskerville, R., & Kaul, M. (2023). Managing compliance with privacy regulations through translation guardrails: A health information exchange case study. Information and Organization, 33(1), Article 100455. https://doi.org/10.1016/j.infoandorg.2023.100455
2) Barbaria, S., Jemai, A., Ceylan, H. İ., Muntean, R. I., Dergaa, I., & Boussi Rahmouni, H. (2025). Advancing compliance with HIPAA and GDPR in healthcare: A blockchain-based strategy for secure data exchange in clinical research involving private health information. Healthcare, 13(20), 2594. https://doi.org/10.3390/healthcare13202594
3) Batool, A., Zowghi, D., & Bano, M. (2025). AI governance: A systematic literature review. AI and Ethics, 5, 3265–3279. https://doi.org/10.1007/s43681-024-00653-w
4) Bhat, S. (2023). The effectiveness of internal controls in preventing fraud and financial misconduct. Journal of Law and Sustainable Development, 11(5), e1178. https://doi.org/10.55908/sdgs.v11i5.1178
5) Bodnari, A., & Travis, J. (2025). Scaling enterprise AI in healthcare: The role of governance in risk mitigation frameworks. npj Digital Medicine, 8(1), Article 272. https://doi.org/10.1038/s41746-025-01700-4
6) Chen, Y., Li, B., & Huo, B. (2025). Building operational resilience through digitalization: The roles of supply chain network position. Technological Forecasting and Social Change, 211, Article 123918. https://doi.org/10.1016/j.techfore.2024.123918
7) Conduah, A. K., Ofoe, S. H., & Siaw-Marfo, D. (2025). Data privacy in healthcare: Global challenges and solutions. Digital Health, 11, Article 20552076251343959. https://doi.org/10.1177/20552076251343959
8) Freeman, S., Wang, A., Saraf, S., Potts, E., McKimm, A., Coiera, E., & Magrabi, F. (2025). Developing an AI governance framework for safe and responsible AI in health care organizations: Protocol for a multimethod study. JMIR Research Protocols, 14(1), Article e75702. https://doi.org/10.2196/75702
9) Harel, Y., & Carmeli, A. (2025). A strategic cybersecurity oversight framework: A board’s imperative. Journal of Cybersecurity, 11(1), tyaf021. https://doi.org/10.1093/cybsec/tyaf021
10) Hassan, M., Borycki, E. M., & Kushniruk, A. W. (2025). Artificial intelligence governance framework for healthcare. Healthcare Management Forum, 38(2), 125–130. https://doi.org/10.1177/08404704241291226
11) Iyer, V. R., & Babu, K. (2025). Resilience at the core: Enhancing cyber-resilience and cybersecurity practices in healthcare sector. Journal of Contingencies and Crisis Management, 33(3), e70061. https://doi.org/10.1111/1468-5973.70061
12) Luidold, C., & Jungbauer, C. (2024). Cybersecurity policy framework requirements for the establishment of highly interoperable and interconnected health data spaces. Frontiers in Medicine, 11, 1379852. https://doi.org/10.3389/fmed.2024.1379852
13) Mojtahedi, A., & Zhou, L. (2024). Information technology internal control material weaknesses in financial reporting: Categories, trends, associations, and industry effects. International Journal of Accounting Information Systems, 53, Article 100679. https://doi.org/10.1016/j.accinf.2024.100679
14) Olorunlana, T. J. (2024, June). Securing healthcare data in the cloud under HIPAA and NIST frameworks. International Journal of Science, Architecture, Technology and Environment, 1(3), 61–80. https://doi.org/10.63680/ijsate032528.07
15) Osifowokan, A. S., Ahmed, Z., Adukpo, T. K., & Mensah, N. (2025). Enhancing data compliance in the United States healthcare system: Addressing challenges in HIPAA and HITECH Act implementation. EPRA International Journal of Multidisciplinary Research, 11(4). https://doi.org/10.36713/epra21263
16) Panful, B., Apaflo, B., & Hutchful, N. (2025). Cyber-physical systems under threat: A case-study review of recent SCADA attacks in the U.S. utility sector. Sarcouncil Journal of Engineering and Computer Sciences, 4(12), 104–117. https://sarcouncil.com/download-article/SJECS-613-2025-104-117.pdf
17) Panful, B., Apaflo, B., & Hutchful, N. (2026). From compliance to culture: Assessing organizational cybersecurity readiness in public vs. private U.S. utility companies. EPRA International Journal of Research and Development, 11(1), Article 18669.
https://doi.org/10.36713/epra25731
18) Papagiannidis, E., Mikalef, P., & Conboy, K. (2025). Responsible artificial intelligence governance: A review and research framework. The Journal of Strategic Information Systems, 34(2), Article 101885. https://doi.org/10.1016/j.jsis.2024.101885
19) Pilosof, N. P., Welcman, Y., Barrett, M., Oborn, E., & Barrett, S. (2025). Building digital resilience: Leading healthcare transformation through an online community. Frontiers in Digital Health, 7, 1656804. https://doi.org/10.3389/fdgth.2025.1656804
20) Subramanian, H., Sengupta, A., & Xu, Y. (2024). Patient health record protection beyond the health insurance portability and accountability act: Mixed methods study. Journal of Medical Internet Research, 26, Article e59674. https://doi.org/10.2196/59674
21) Tabansky, L., & Lichterman, E. (2025). PROGRESS: the sectoral approach to cyber resilience. International Journal of Information Security, 24, Article 18. https://doi.org/10.1007/s10207-024-00910-3
22) Taiwo, P. O., Akoto-Bamfo, D., Tetteh-Kpakpah, C., Panful, B., & Oware, D. (2025). Evaluating the role of cybersecurity audits in protecting the US capital market. World Journal of Advanced Research and Reviews, 25(2), 974–980. https://doi.org/10.30574/wjarr.2025.25.2.0183
23) Taherdoost, H. (2022). Understanding cybersecurity frameworks and information security standards—A review and comprehensive overview. Electronics, 11(14), Article 2181. https://doi.org/10.3390/electronics11142181
24) Tetteh-Kpakpah, C., Adjaottor, S., & Donkor, A. A. (2025). Mitigating cyber threats through cybersecurity audits and adaptive defense: A case study on financial institutions. EPRA International Journal of Economic and Business Review, 13(7). https://doi.org/10.36713/epra23002
25) Wang, W., Sadjadi, S. M., & Rishe, N. (2024, May). A survey of major cybersecurity compliance frameworks. In 2024 IEEE 10th Conference on Big Data Security on Cloud (BigDataSecurity) (pp. 23–34). IEEE. https://doi.org/10.1109/BigDataSecurity62737.2024.00013
26) Wu, T.-H., Huang, S. Y., Chiu, A.-A., & Yen, D. C. (2024). IT governance and IT controls: Analysis from an internal auditing perspective. International Journal of Accounting Information Systems, 52(Suppl. C), Article 100663. https://doi.org/10.1016/j.accinf.2023.100663
Downloads
Published
Issue
Section
License
Copyright (c) 2026 Matilda Konotey , Daniel Akoto- Bamfo , Godson Teye Apaflo (Author)

This work is licensed under a Creative Commons Attribution 4.0 International License.